UK Cyber Resilience in 2026: Why Manual-First Penetration Testing Is Your Smartest Move
Discover how UK businesses can strengthen cyber resilience in 2026 with manual-first penetration testing, vulnerability…
Noor Fatima9 Sept 2026
Mobile Application Security
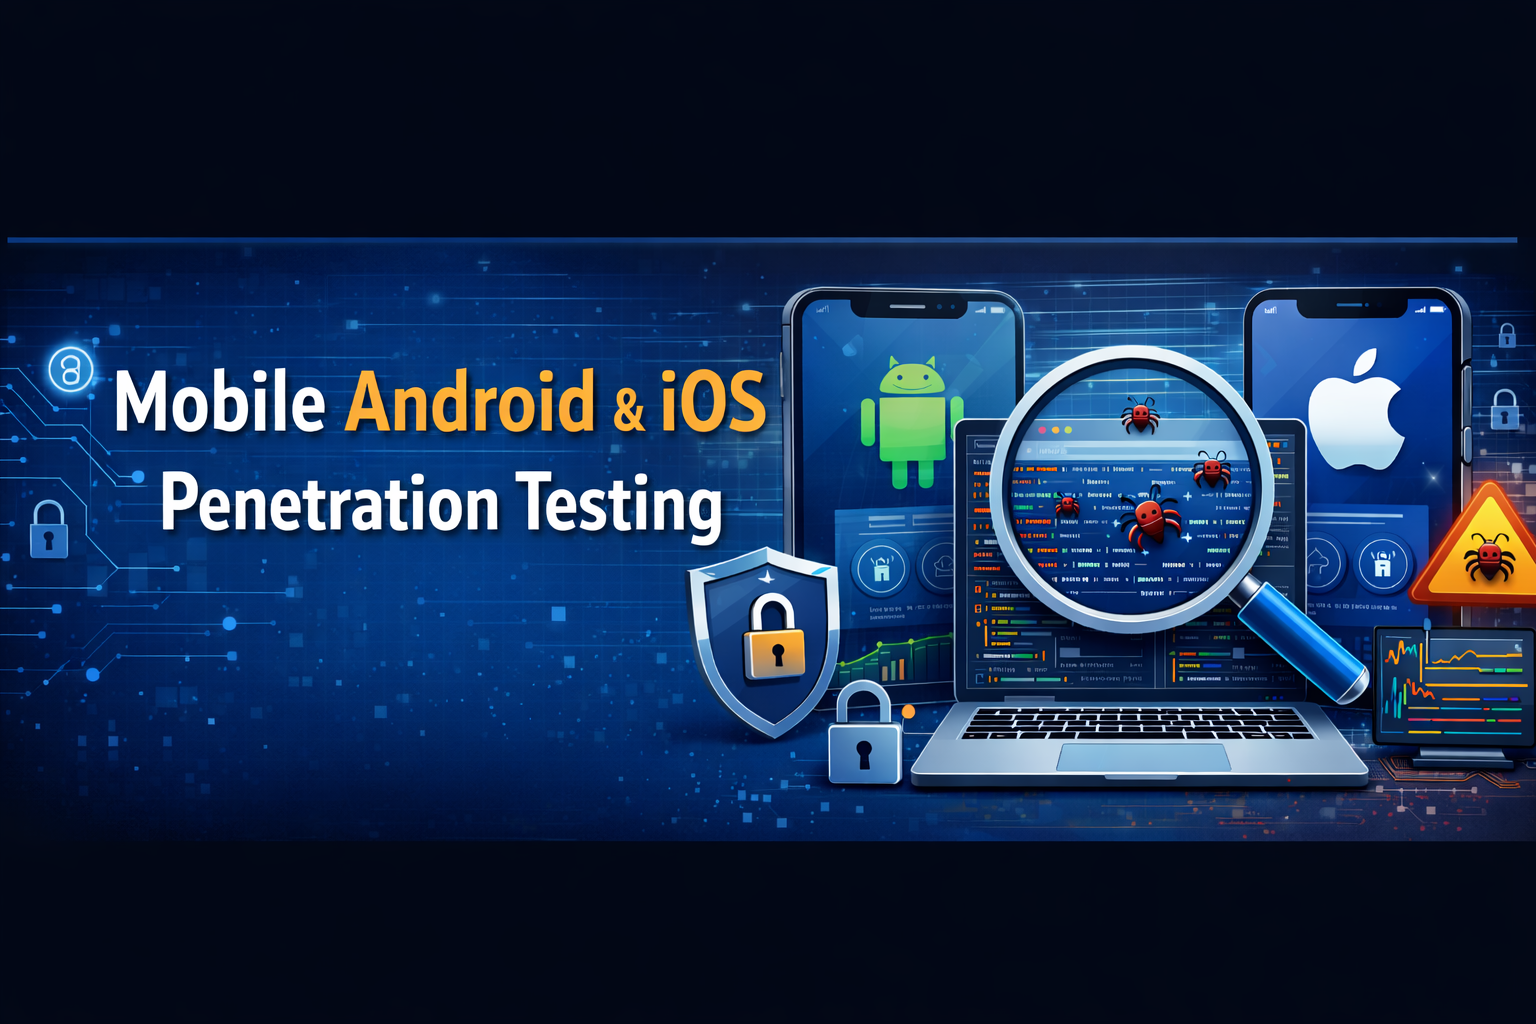
Android and iOS Penetration Testing of mobile devices.
The contemporary business is being catalyzed by mobile applications. The customers purchase or sell, move funds, save information, and manage services using apps each day. This ecosystem is dominated by Android and iOS. The attack surface increases with the increase in usage.
These criminals have been exploiting mobile applications. They take advantage of poor authentication, flawed APIs, as well as inadequate data storage. Lots of companies think that they have built-in platform security. It is not.
This is the reason mobile application penetration testing has been necessary.
A systematic mobile threat test will aid organizations in identifying lurking vulnerabilities before hackers. Vulnerabilities do not get disabled in a production environment without active testing. Cases of data breach, loss of money, and the breach of compliance can be experienced as a result of such exposure.
Android and iOS have different security architectures. They are to be tested using specialized knowledge.
Simple testing tools are unable to detect profound mobile defects. Firms require dedicated Android penetration testing and organized iOS testing services in order to ensure the strength of the applications.
There are mobile apps that are linked to APIs, cloud servers, and third-party libraries. Where once a connection is made, another connection is created. In the instance where API endpoints are not validated, attackers can intercept or otherwise modify data. It is at this point that API security testing of mobile apps is incredibly essential.
There are numerous vulnerabilities that are consistent with the OWASP mobile testing guide, which proposes general mobile risks. These include:
These threats are ignored, and sensitive information is revealed. Hackers can have access to any of your private data. credentials, executing malicious code, or escalating privileges inside the app would be easy to get.
Other organizations make use of automated scanners alone. Some of them carry out single reviews prior to going to circulation. Both approaches leave gaps.
The mobile apps are updated regularly. New functionality poses new risks. Weaknesses are not detected unless they are constantly validated.
An efficient mobile app vulnerability testing is more than scanning. It is a combination of static analysis, dynamic testing, and manual verification. It checks the performance of the app in the event of actual attacks.
Adversarial behavior is gained by security professionals. They attempt bypasses. They check authentication processes. They search encrypted traffic. This fulfilment displays errors that can not be detected by automation.
A successful Android app security audit looks into:
Correspondingly, the iOS app penetration testing is aimed at:
Every platform requires different approaches.
Mobile Security Failure and Its Business Impact.
There are severe repercussions of mobile security attacks.
Customer information may be revealed in case of a breach. That will result in financial fines and legal investigation. Data protection standards are imposed with strict measures by regulatory bodies. Lack of adherence is hurtful to credibility.
The other risk is of removing the app stores. In case an application does not pass the security review standards, it might be suspended. Such a distraction directly impacts the revenue.
Customer trust is fragile. One event is enough to attract adverse publicity. Users can delete the application.
Costs are also increased during operational downtime. Responding to the incident is resource-consuming. Business cannot go on as fast as forensic investigations take their time.
The penetration testing of the mobile applications is proactive to reduce these risks. It defines vulnerabilities prior to exploitation. It supports compliance. It enhances customer assurance.
Mobile Android and iOS Penetration Testing Involvement. Mobile Android and iOS Penetration Testing is a regulated procedure.
First of all, there is reconnaissance carried out by experts. They know the architecture of the application and the flow of data.
Second, they do code analysis at rest. This is a step that identifies insecure and vulnerable coding practices.
Third, the dynamic testing tests the behavior at runtime. Analysts monitor traffic. They check the handling of sessions. They make an attempt at being exploited under regulated circumstances.
Fourth, the testers attempt to replicate attack scenarios that are congruent with the OWASP mobile testing guide. They imitate real-world patterns of threats.
This strategy also favours secure mobile application development. Remediation guidelines are elaborated to development teams. Security is included in the software lifecycle, and not an afterthought.
A full mobile threat assessment also appraises backend systems. A significant number of violations are done via unprotected APIs. Thus, the security testing of the mobile application API is beneficial to make sure server-side validation is comparable with the mobile security.
Testing of the security should be continuous. Every update has to be validated. Every change in configuration requires oversight.
Enhancement of Mobile Security by Dynamic Planning. Contemporary businesses have mobile-first strategies. Security should also be comparable to that mindset.
Companies that invest in organized mobile application entry penetration testing receive:
Assumptions should not be made as far as mobile security is concerned. It must rely on validation.
The delayed testing by businesses enriches their risk profile of risks. Public apps are being scanned continuously by attackers. They scan weak ends and leak information.
Defense posture is changed as a result of proactive security testing. It is no longer in the contamination reactive incident response but in proactive control.
Selecting the Right partner in security. Technology is not enough of a guarantee of protection. Expertise matters.
A partner is confident in knowing platform-specific risks. They deliver reports that are practical and not general.
Pluto Cyber Security is a multidimensional Android penetration testing company and state-of-the-art iOS security testing company committed to serving the current mobile environment.
Our approach includes:
We concentrate on actual business delivery. Our professionals are both technical and tactical. We assist companies in enhancing safe mobile phone app development throughout the design process to deployment.
In the event that your organization is developing, maintaining, or distributing mobile applications, then proactive security verification is required.
Waiting until a breach comes to reveal some hidden weaknesses.
Pluto Cyber Security is available today at +44 7481 912177 or contact@plutosec.uk.
To book your professional mobile threat assessment today.
Protect your applications. Protect your users. Protect your business.
Android and iOS Penetration Testing Mobile Android and iOS Penetration Testing is a formalized security procedure that helps in establishing weaknesses in the mobile applications, which may be harnessed by the attackers.
Android penetration testing services assist in uncovering code vulnerabilities, insecure storage, and permission defects that have the potential to expose sensitive user information.
The security testing of the iOS is assessed based on keychain security, certificate validation, secure coding, and runtime security.
The security testing of mobile applications API ensures that request validation is fulfilled by the backend systems and that it does not manipulate data or grant unauthorized access.
Well-organized mobile app vulnerability testing can assist groups in resolving vulnerabilities earlier and establishing healthy mobile app development.
Written by
Admin
Your email won't be published.
No comments yet. Be the first to comment!
Keep reading
Discover how UK businesses can strengthen cyber resilience in 2026 with manual-first penetration testing, vulnerability…
The UK Cyber Security and Resilience Bill is moving through Parliament while NIS2 reshapes compliance across Europe. Here is what…
 AI Security & Cybersecurity
To build a secure future, organizations must look beyond defense. Achieving cyber resilience in 2026 requires a strategic shift…
Get started
Tell us what you need tested. We reply with honest guidance and a fixed-scope quote, usually within one business day.