UK Cyber Resilience in 2026: Why Manual-First Penetration Testing Is Your Smartest Move
Discover how UK businesses can strengthen cyber resilience in 2026 with manual-first penetration testing, vulnerability…
Noor Fatima9 Sept 2026
Artificial Intelligence Security
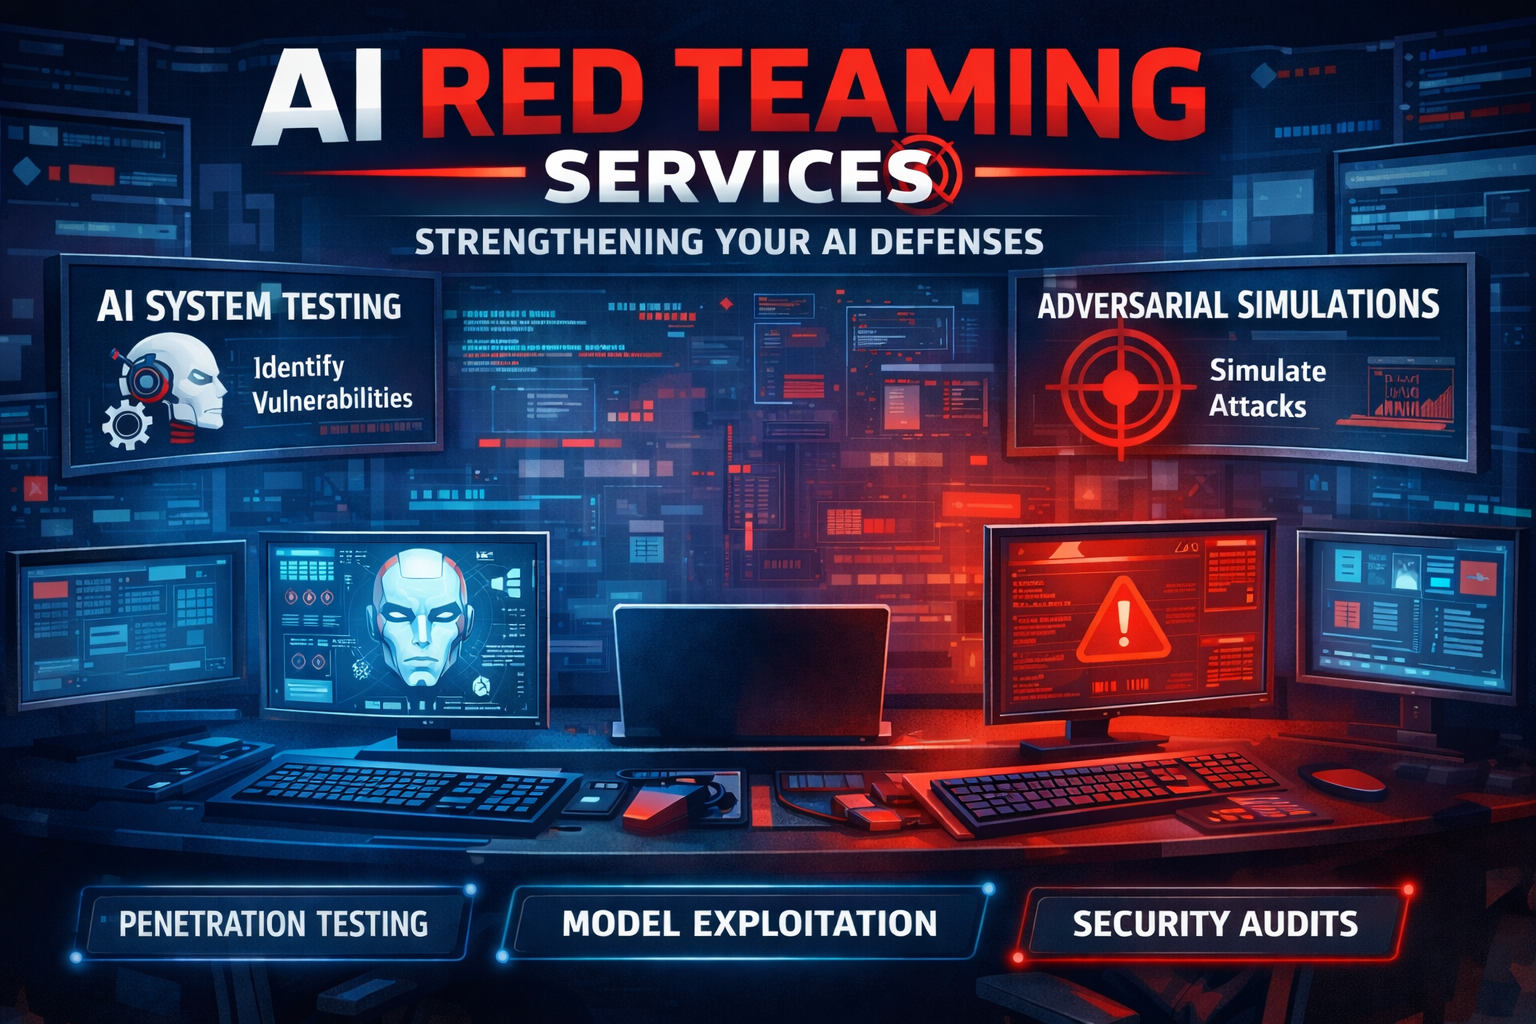
The modern digital systems are quickly changing as a result of artificial intelligence. Organizations today are using AI models to automate decisions, to analyze information, and to enhance customer experiences. But with the rise in the use of AI, so does the security risk.
AI systems present a new front in the form of attack, and normal security testing is incapable of dealing with it. Unless experimented on with a red team, one can never be sure of the appropriate machine learning successes and thus the presence of the hidden flaws.
Organizations today also use specialized AI red team testing and AI model penetration testing as a means of finding vulnerabilities before attackers can find them. These positive security practices assist organizations in securing their AI systems against manipulations and misuse.
The Growing Security Risks in AI Systems
Computers generate artificial intelligence (AI) to work with large amounts of data. They also come up with rulings that affect financial dealings, healthcare programs, as well as the operations of an enterprise.
The consequences of the attackers manipulating these models may be drastic. The input materials can be intrusive and used to twist the AI systems into incorrect results, reveal classified data, or evade risk management.
This increased threat has put into greater demand the generation of AI security testing and the systematic testing of AI adversarial. Security personnel need to test the behavior of AI systems under unfriendly environments.
In companies using large language models, it should also be remembered that it needs to take into account the concept of LLM red teaming to assess how the AI reacts to malicious associations and opposite commands
Why Traditional Security Testing Is Not Enough
The conventional approach to cybersecurity interventions dwells on software vulnerabilities. AI systems work in a different way since they are sensitive to data and change with time.
Attackers may use this learning process in data poisoning, prompt injection, or model manipulation. These attacks are against the logic of AI and not the application code.
Such threats cannot be identified with the use of standard penetration testing instruments. The security teams thus make use of AI simulation of attacks to know how the attackers may hack into intelligent systems.
Formal AI red team testing can help practitioners to develop realistic adversarial conditions and reveal the latent flaws of AI environments.
What Is AI Red Teaming
AI red teaming is a high-level horror test that determines the resilience of artificial intelligence. It is a type of hacking that engages ethical hackers who imitate complex attacks on AI models, training data, and deployment settings.
The aim is to establish weak aspects before they are found by malicious agents. Throughout the process, intelligence workers conduct managed AI adversarial assessment and smart assault simulations.
Such simulations involve immediate manipulation, antagonistic input generation, and model behavior. This kind of testing will make organizations know how attackers can abuse their AI systems.
Advanced AI model penetration testing also determines the interactions between AI and APIs, applications, and underlying infrastructure.
The Role of LLM Red Teaming
Massive language models have formed an important part of contemporary AIs. Some of their use cases are chatbots, automation, analytics, and customer engagement by businesses.
These models, however, can be exploited with the help of well-engineered prompts. Hackers will possibly endeavor to circumvent security regulations or get sensitive data stored in the AI systems.
This is where LLM red teaming is necessary. The tests of the security experts involve the linguistic models in response to malicious queries, deceptive instruction or, or adversarial queries.
Upon a simulated attack of an AI, organizations will be able to test the safety and security of their AI systems when pressure is applied to them.
Insecure AI Systems Business Risks
Weak AI security may expose the organizations to grave risks in terms of operations. A weak AI model might produce incorrect results, disclose sensitive information, or interrupt automated services.
These derailments are capable of ruining brand names and popularity. The regulatory scrutiny can also be a problem for businesses when AI systems inadequately process sensitive data.
The use of AI models in decision-making systems in finance, healthcare, and government may also lead to security concerns. This danger shows the value of generative AI in proactive security testing.
Through ongoing AI red team experiments, companies should be able to identify vulnerabilities at the outset and mitigate operational risks.
The way AI Attack Simulation enhances security
Good testing of security should be able to mimic a real-world attacker. AI attack simulation enables a security team to test the response of AI models to unfavorable conditions.
Experts recreate different attacks, such as adversarial attacks, data manipulation attacks, and model evasion attacks. The tests are used to determine the weaknesses that would not be established in an ordinary test.
Organizations are able to test their AI models under stress in structured AI adversarial tests. This knowledge can assist security teams to bolster security, as well as enhance the resistance of models.
Such simulations, joined with AI model penetration testing, give an in-depth analysis of AI security.
Red Team AI Application in Security Plans
The use of AI in organizations requires the aspect of security testing as a part of the development cycle. Delays may expose systems to severe risks before their deployment.
Regular AI red teaming tests should be done by security teams so that models can be resistant to new threats.
The effective strategies of testing are:
Such practices enhance the security testing of generative AI and enhance the overall reliability of AI systems.
The Future of AI Security Testing
Artificial intelligence is bound to develop quickly. Attackers will also evolve better techniques as the models continue to increase in power.
The security teams are thus required to embrace proactive testing. Ongoing AI red team exercise assists organizations to be above the upcoming threats.
The next level of LLM Red teaming and simulated intelligent AI attack will be instrumental in the protection of AI in industries.
The organizations that invest in structured AI model penetration testing will be able to construct increasingly secure and trustworthy AI environments.
Conclusion
The power of the opportunities brought by artificial intelligence opens up innovation opportunities, yet the innovations present new cybersecurity challenges. AI systems should be put under scrutiny to make them secure and reliable.
Active AI red teaming can assist companies in identifying weaknesses and preventing attacks by criminals. The security teams can exercise hands-on AI red team testing to recreate realistic adversarial situations.
Sophisticated AI model penetration testing, LLM red teaming, and full generative AI security testing are what bring visibility to protect intelligent systems.
Companies that put these practices into core focus can use AI technologies safely, yet ensure efficient cybersecurity barriers.
FAQs
What is AI red teaming?
AI red teaming is a method of security testing used to perform testing on the strength of artificial intelligence systems by experts who mimic cyber attacks.
What is the AI model penetration testing?
AI model penetration testing analyzes machine learning models on vulnerabilities such as data manipulation, adversarial model input, and prompt injection attacks.
What is the significance of LLM red teaming?
To control safe and secure behavior of large language models, LLM red teaming evaluates the models on malicious prompts and adversarial queries.
What is generative AI security testing?
Generative AI security testing is an assessment of the security and dependability of AI models in the content creation, automation, and decision-making processes.
Written by
Admin
Your email won't be published.
No comments yet. Be the first to comment!
Keep reading
Discover how UK businesses can strengthen cyber resilience in 2026 with manual-first penetration testing, vulnerability…
The UK Cyber Security and Resilience Bill is moving through Parliament while NIS2 reshapes compliance across Europe. Here is what…
 AI Security & Cybersecurity
To build a secure future, organizations must look beyond defense. Achieving cyber resilience in 2026 requires a strategic shift…
Get started
Tell us what you need tested. We reply with honest guidance and a fixed-scope quote, usually within one business day.