 AI DevSecOps Security
AI DevSecOps & Secure AI Deployment
The role of AI is now firmly embedded in the most current applications, including automation systems or even customer-facing…
Admin26 Mar 2026
cyber security
However, cybersecurity is mostly viewed as a technical issue; in numerous real-world attacks, however, the weak link is not the system. It is the people using it. Unless they are well prepared, employees, vendors, and even management can act as entry points for attackers.
Social engineering attacks are on the increase in the UK among businesses. These breaches are not based on the hacking of systems. Rather, they depend on the manipulation of the behavior of human beings. This increases their difficulty to be caught and the ease with which they are carried out.
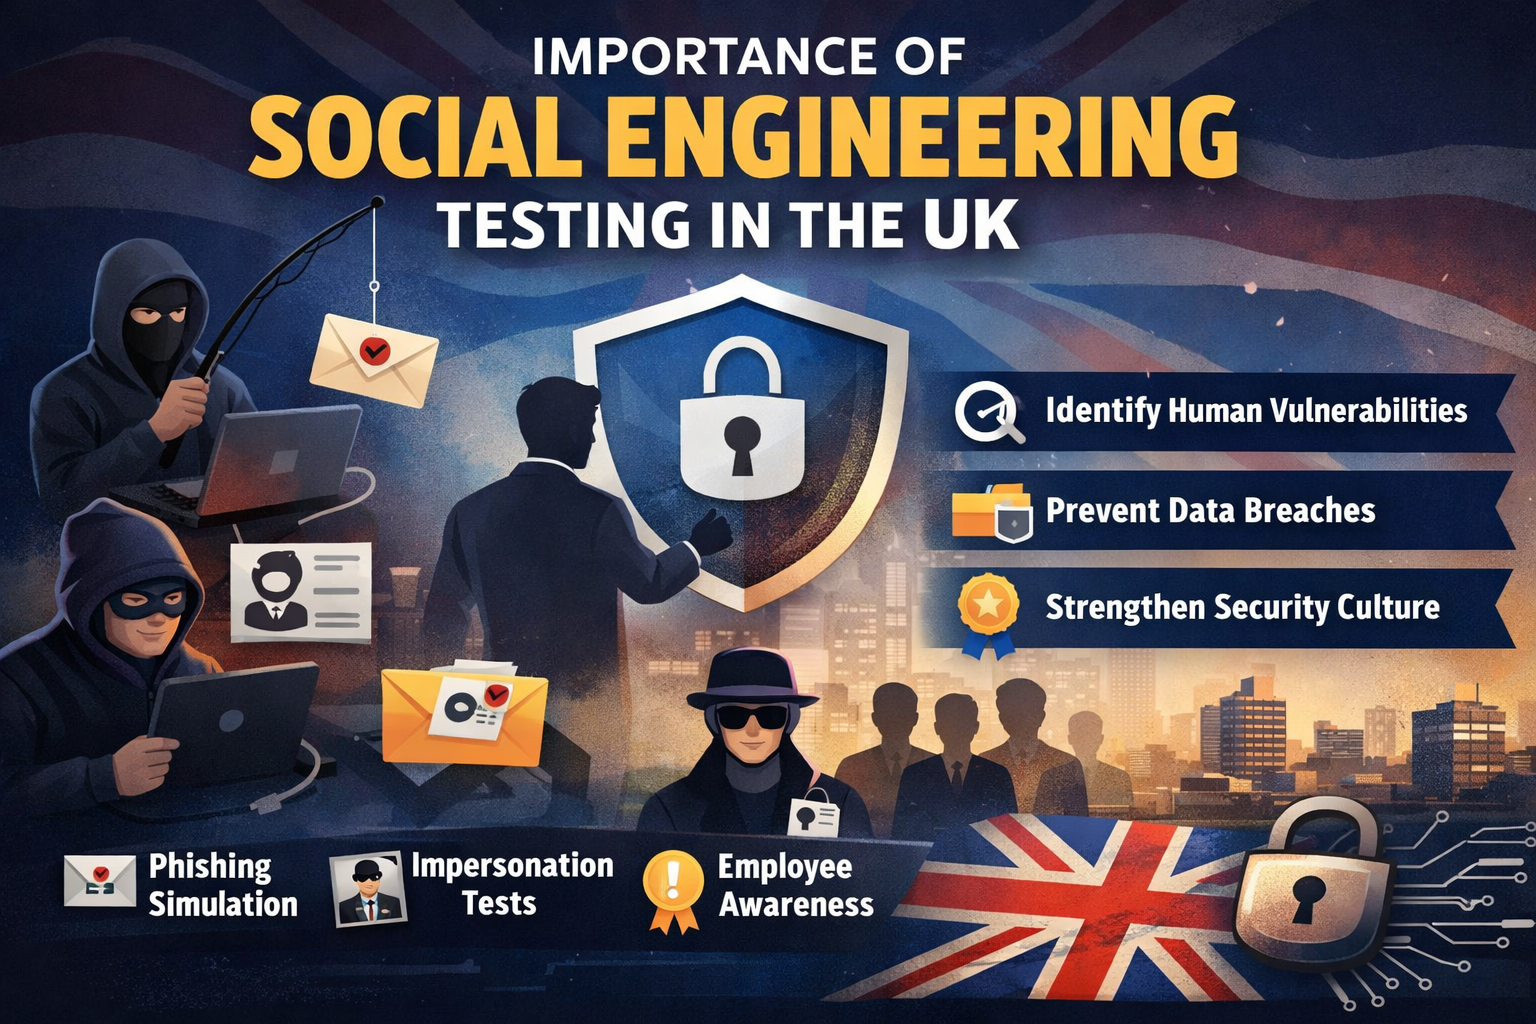
That is why Social Engineering Testing UK has become an obligatory element in contemporary security policies. It assists organizations in determining the reaction of employees to actual threats and where they require improvement.
These are the tests that mostly feature phishing simulation UK, bogus login pages, or impersonation threats. The emails received by the employees can seem valid and are aimed at determining whether the employees practice securely or not.
This form of testing is based on human factor cybersecurity, which is neglected in most cases in security programs. By determining the response that people display during a time of pressure, companies are in a position to defend themselves better.
What Social Engineering Test Looks Like A social engineering test aims to mimic the real attack activity as much as it is possible. It is not random. It takes into consideration the trends that attackers really follow. As an example, an employee can be sent an email that has the appearance of the mail being sent by a reputable source. The email can be requesting them to either open a link, download a file, or give them login information. This is an ordinary type of email testing. On another scale, the attackers can fake either inside staff or third-party relations. The tests are included in a planned audit of social engineering in the UK, in which the behaviors of employees are tested through methods of different attacks. This is aimed at monitoring their reactions among employees, not to fault them. The results assist organizations to learn where they require stiffer controls or more training. WHY SOCIAL ENGINEERING ATTACKS ARE RISING IN THE UK UK has been experiencing a gradual rise in phishing and impersonation attacks. Hackers are always looking to exploit workers, which is especially because of the digital tools used in businesses and the models of working remotely. Most organizations are huge investors in technical security and do not focus on human behavior. This leaves a loophole that is used by attackers. Phishing black hat testing usually shows that well-trained teams can succumb to well-prepared messages. Urgency, authority, and familiarity used by attackers have been found to raise success rates. These attacks may result in data breaches, financial loss, and damage to reputation without regular testing and awareness campaigns. Why the Social Engineering Test IS Worthy of Conducting The occurrence of Social Engineering Testing UK has concrete and quantifiable advantages. It assists the organizations to avoid assumptions and make considerable advances in reality. The businesses can know who among the employees is more susceptible to attacks and where improvements can be made. This will enable them to come up with relevant security training UK courses rather than general beginner courses. It also aids in testing the ability of the awareness programs that are going on in the UK. If the errors made by employees remain the same, it is a sign that the existing methods of training are not effective. By filling these gaps, the organizations can mitigate risk and enhance the general state of security. WHY START NOW The postponement of social engineering testing raises the risk. Bad people are continuously improving on their techniques, and those businesses that fail to keep up get targeted easily. The more time it takes an organization to go through without testing, the higher the chances that vulnerabilities are concealed. One successful phishing case may have severe consequences. The time to begin is to enable businesses to understand what risks are there very soon and correct them before the actual attack takes place. It also creates a culture of awareness whereby employees are made active members of the security process. Creating Good Workplace Security Awareness Amongst Employees The initial barrier to social engineering attacks is that of the employees. But consciousness does not arise out of the training that people attend a single time. It takes constant effort. The regular security training in the UK, as well as the practical simulators, would assist employees in identifying threats and reacting appropriately. This involves detecting suspicious emails, not posting on unsafe links, and reporting any possible occurrences. By considering employee security awareness in the UK, security will be integrated into day-to-day operations rather than a policy regulation. Prevention Strategies of Social Engineering Detection and prevention of social engineering attacks involve having an amalgamation of technical and training, as well as testing. Regular social engineering audit UK exercises should be carried out by the organizations to determine the weaknesses. Targeted training and better security policies should come after these tests. There is also good social engineering prevention, like email filtering, access control, and suspicious activity monitoring. Technical measures are not sufficient, however. The staff should be up to date to detect and act upon threats. The Business Impact of Ignoring Human Risk Neglecting the risks that are associated with humans may be problematic. One successful attack may result in unauthorized access, exposure of data, or financial fraud. Other than the loss of money, businesses might experience regulatory problems and reputation. Trust is paramount in competitive markets such as the UK. The loss of such trust may be long-term. The implication of the above is that by investing in Social Engineering Testing UK, it is simpler to mitigate the occurrence of such outcomes because the threat is dealt with before it can be taken advantage of. Test Your People Before Attackers Do Most organizations expect their employees to be ready, yet they do not test them; therefore, it is just an assumption. The true security mode is gained through knowing how individuals act on the ground. Our Social Engineering Testing UK at Pluto Cyber Security is an experience that simulates a real-world attack scenario. We do not rely on theory. We put your employees to the test in realistic situations and give you a clear picture of how to improve your security. In case your organization has never tested its human security layer, then there is even a risk. Pluto Cyber Security. Contact the company at +44 7481912177 or [email protected] to reinforce your security. Hackers are already attacking your people. Whether or not you are prepared is the question. FAQs What is the Social Engineering Testing UK? It is a security test that measures the reaction of employees towards simulated attacks, such as phishing and impersonation. What is phishing simulation UK? This is an email response and awareness test by sending controlled test emails to the employees. What is threatening about social engineering attacks? They attack human behavior, and they are therefore more difficult to notice compared to technical attacks. What should be the frequency of businesses' testing? It is suggested that regular testing should be conducted to align with the changing threats and enhance awareness. What does social engineering prevention aim for? The social engineering prevention will focus on minimizing human risks by testing, training, and implementing security measures.
Written by
Admin
Your email won't be published.
No comments yet. Be the first to comment!
Keep reading
AI DevSecOps SecurityThe role of AI is now firmly embedded in the most current applications, including automation systems or even customer-facing…
 cyber security
Every day, cyber attacks are on the rise. The companies have been exposed to ransomware.
 Cloud Security
Cloud applications have now become the drivers of most of the modern applications.
Get started
Tell us what you need tested. We reply with honest guidance and a fixed-scope quote, usually within one business day.